CTO Community India: Software Vulnerability Assessment in the Era of AI
The CTO Community India recently hosted its fifth milestone series, pivoting from its previous explorations of AI , Quantum and Startups to the pressing frontier of Cyber Security in the AI Era.
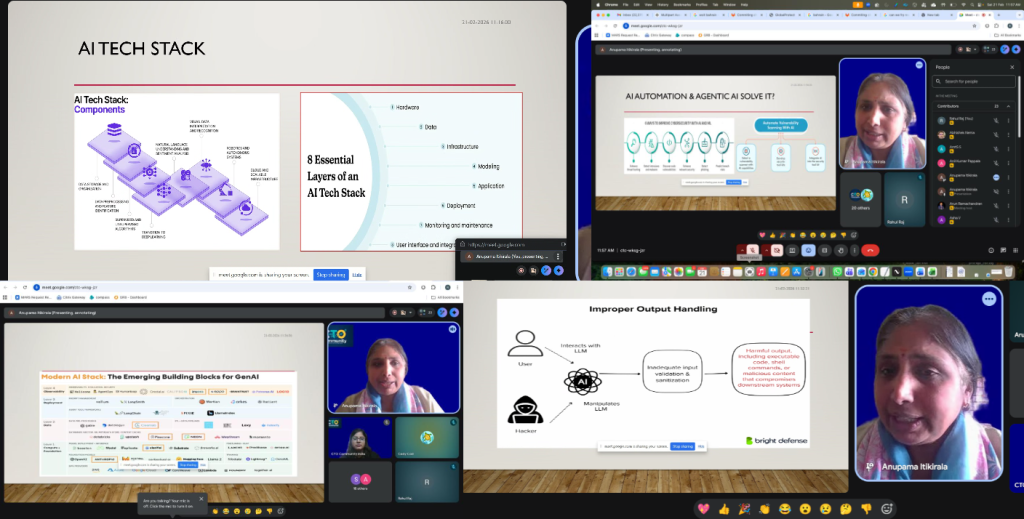
Led by Anupama Itikirala, Founder of Mayuk Enterprises, and moderated by Richa Kumari , the session provided a masterclass in navigating the “new normal” where code is generated in seconds, but vulnerabilities can last a lifetime.
The Session Agenda:
- Career Resilience: Anupama’s 30-year journey from Enterprise Architect to a “Tech for Good” consultant.
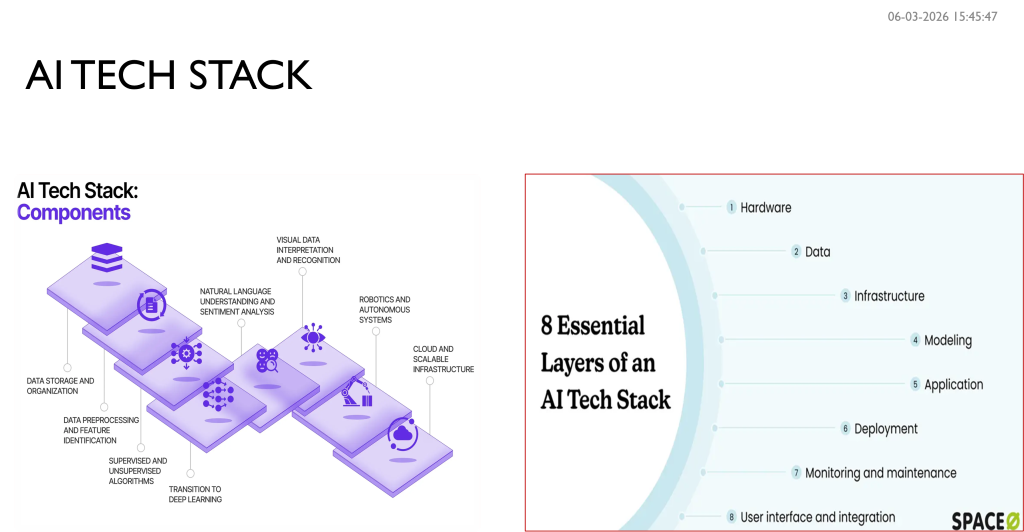
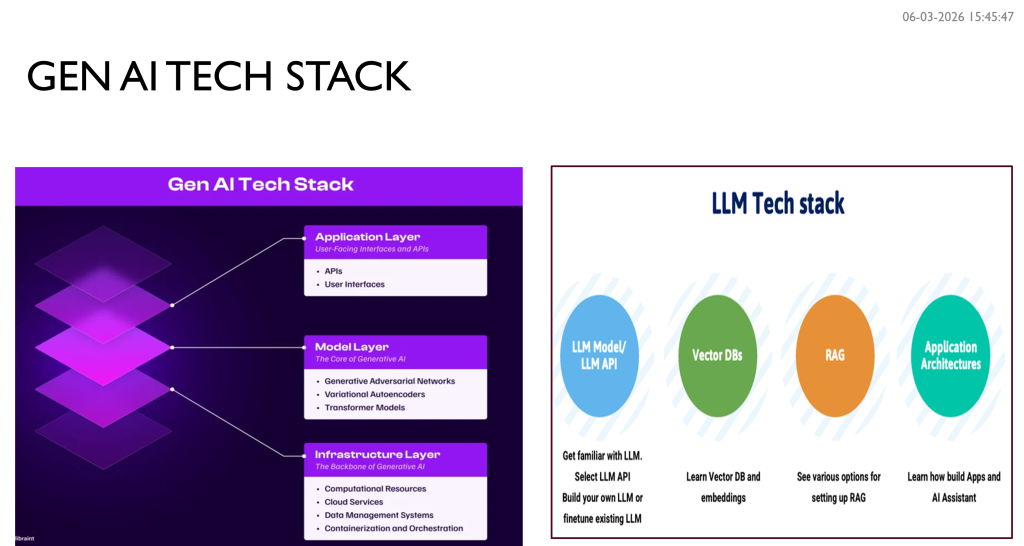
- The New Stack: Understanding vulnerabilities in the Generative AI architecture (Infrastructure vs. Model vs. App layer).
- The “Why” of Security: A panel discussion on why automated cycles still need human-in-the-loop governance.
- Deep Dive: Decoding the OWASP Top 10 for LLMs (Prompt Injection, Model Poisoning, etc.).
- Demo: A first look at Garuda, a cost-effective, NLP-driven code scanning tool for startups.
A Journey of Resilience and “Tech for Good”
Anupama Itikirala opened the session with a powerful personal narrative. With 30 years in the industry—including stints at Intel, Oracle, and GE—she shared her journey of restarting her career after a 2016 break.
Now a celebrated consultant and mentor, Anupama’s work is driven by “Tech for Good.” she emphasizes that technology must be inclusive, ethical, and, above all, secure.
The New Threat Landscape: Gen AI & the OWASP Top 10
The transition from predictive analytics to Generative AI has drastically expanded the attack surface. Anupama, broke down the critical evolution of the tech stack.
Key Technical Takeaways:
- Vulnerability vs. Risk: Vulnerability is the weakness; Threat is the actor; Risk is the impact.
- The LLM Vulnerability Shift: Unlike traditional relational databases, Gen AI relies on unstructured data and complex “orchestration” layers, creating new backdoors.
- The OWASP Top 10 for LLMs: The session highlighted critical risks:
- Prompt Injection: Malicious inputs designed to override AI safety guards.
- Model Poisoning: Manipulating training data to create systemic biases or backdoors.
- Excessive Agency: Granting AI “agents” too much power without a “human-in-the-loop” to verify actions.
“Security is no longer a ‘nice-to-have’ in industries like automotive, a Bluetooth backdoor isn’t just a data leak; it’s a life-threatening risk.” — Abhishek Nema (CTO Community Member)
Innovation Spotlight: Project Garuda
In a standout segment, she demonstrated Garuda, her custom-built code scanning tool. Designed specifically for small companies and startups that find enterprise licensing (like SonarQube) prohibitive, Garuda offers:
- NLP-Driven Heuristics: Uses programming language parsers to build abstract syntax trees.
- Real-time Intelligence: Syncs with the National Vulnerability Database (NVD) twice daily.
- Cost-Effectiveness: A service-based model that prioritizes resource support over expensive tool licenses.
Looking Ahead: What’s Next for the Community?
As the session concluded, the room buzzed with ideas for future deep dives. The community is looking toward:
- Testing LLMs: Addressing the “Black Box” nature of model outputs.
- RAG Implementation: Refining Retrieval-Augmented Generation for better information reliability.
- Indic Languages: Solving the security gap for non-English NLP databases.
A Note of Gratitude
We extend a heartfelt Thank You to our guest speaker, Anupama Itikirala, for sharing her deep technical expertise and inspiring career journey. Her passion for mentorship and “tech for good” is a beacon for our CTO community.
We also thank our active participants, whose insights into business continuity and automotive safety added invaluable layers to the discussion. It is your engagement that makes these sessions a powerhouse of collective wisdom.
Call to Action: Secure Your Future
Don’t let your innovation be derailed by a late-night security alert.
Join the Next Deep Dive: We are currently planning sessions on LLM Testing and RAG Implementation. Stay tuned for the invite!
Adopt “Secure by Design”: Whether you are a solo founder or an enterprise lead, integrate security filters and “human-in-the-loop” checkpoints today.
We encourage all members to adopt “Secure by Design” principles—especially those in the startup phase where ROI often overshadows safety.
Been playing on 80jili.ph for a while now. Decent selection of games, nothing too crazy. Give it a shot, could be your lucky day: 80jili.ph
Looking for the PHL63 sign in? Got you covered! Here’s the direct link to avoid scams: phl63 sign in. Play safe, everyone!
The download process of Awin is just so easy and quick I really like it. You can also test it here: tải awin
Heard about ‘b66club’? A friend recommended it, and so far, it’s been pretty good. The community seems active. Give it a try here: b66club
Hey guys, just checked out 3633betlogin and it’s pretty smooth. If you’re looking for a new spot to play, give 3633betlogin a shot. Could be your lucky day!
Yo, 79xgame is on my radar now. I’ve heard good things, going to give it a try tonight. Maybe I’ll see you all there? Check it out: 79xgame
Solid platform with a very user friendly vibe. The loading times are minimal and the rewards are actually attainable. Five stars for aaaplataformabet.
The distinction between vulnerability, threat, and risk—and the warning about excessive agency—really stood out. Garuda’s focus on practical, affordable scanning for startups is especially valuable. I also appreciate the reminder that security needs human oversight, even as automation accelerates.
change song pitch online
The distinction between vulnerability, threat, and risk—and the reminder that AI agents need human oversight—made this especially useful. I also appreciated the focus on Garuda as an affordable option for startups. Clear planning matters in any complex system; even WoW Forever Talent’s build calculator labels unverified preview ranks so players can
wow forever talent
The graphics on this site are amazing and the slots are actually fair. I had a great run last night. You guys should really try dino69slot if you love the thrill.
The session’s point about AI-generated code expanding the attack surface—and the need for human oversight—really stood out. Garuda sounds especially valuable for startups. For teams managing physical inventory or device labels, a browser-based barcode generator can also help create traceable labels without sending data to a server.
free barcode generator
Login is seamless and the account management is very straightforward. No unnecessary hassle just pure gaming. 3lcomlogin is just efficient.
Fast deposits and even faster withdrawals. That is all I really care about and this site delivers perfectly. mustang303login is the real deal.
The distinction between vulnerability, threat, and risk really clarifies why AI security needs more than automated scans. I also appreciated the focus on Garuda’s practical value for startups and the reminder that human oversight matters when AI agents can take consequential actions.
apa reference generator
The distinction between vulnerability, threat, and risk—and the examples of prompt injection and excessive agency—made the session especially practical. I also liked Garuda’s focus on affordable scanning for startups; thoughtful human oversight is essential as AI tools become more capable.
AI clothes changer
The atmosphere of this casino is top notch. It really feels like a premium experience from the moment you sign up. Visit parkjilicasino today.
I love the bonus offers they have for new players. It gave me a great head start. Really happy I found bdl789.
The point that AI-generated code can be produced in seconds while its vulnerabilities may persist for years really stood out. Garuda’s NLP-driven scanning sounds promising for startups, and clear, distinctive text styles could also help make security findings easier to highlight in reports and awareness materials.
Paste Fonts
Finally a site that delivers what it promises. The winning streaks here are unbelievable. Join me at inyoswin and let’s win big!
The distinction between a vulnerability, a threat, and the resulting risk was especially clear, as was the reminder that AI agents need human oversight. For teams discussing topics like prompt injection or model poisoning, Unprompted could also be a handy way to spark fresh research and practice speaking through new security scenarios.
unprompted topic generator
Finally found a site that doesn’t lag during peak hours. The interface is super intuitive and getting started was a breeze. Check out megawin777login if you want a smooth experience.
The discussion of prompt injection, excessive agency, and keeping humans in the loop makes the risks of AI feel very concrete. I also appreciated the focus on practical, affordable security through Garuda—especially for startups that can’t justify enterprise tooling.
motion transfer video generator
The shift toward automated vulnerability scanning in AI workflows is becoming unavoidable, especially as deployment cycles get tighter. The discussion on catching security flaws before models hit production touches on a real bottleneck most engineering leads are trying to balance right now.
On the comms side of our dev updates, I occasionally test tools like Veo 3.1 Video Generator when we need to создать ии видео for quick internal explainers. Feeding it a straightforward prompt like “a glowing server rack flashing amber alerts” gave me a usable five-second backdrop in about two minutes; it won’t replace custom motion design for client-facing work, but it gets the point across during team syncs.
The discussion of prompt injection, model poisoning, and human-in-the-loop oversight makes the risks of generative AI feel very concrete. I also appreciated the focus on accessible scanning tools like Garuda for startups. For event recaps, Burning Bridges AI could turn a lead photo and supporting shots into a short video that brings the session hig
Burning Bridges AI video generator
Vulnerability assessment is definitely getting trickier as more teams plug automated models directly into their development pipelines, especially when edge cases and unvetted dependencies slip through before deployment.
On the media side, when I put together internal awareness clips explaining basic data hygiene, the Kling 4.0 tool I use saves me hours by letting me lock a reference image of a server room so the slow push-in shot stays consistent. It still requires some manual cleanup afterward, but setting that initial keyframe helps keep the shot grounded.
Alanobet88 is a good option if you are looking for somewhere new to play. I found the promotions they offer decent and the layout is easy to negotiate. Go explore! alanobet88
Login is seamless and the customer support is actually helpful. I had a small issue with my deposit and they sorted it out instantly. 90winbet90winlogin
The point about code being generated in seconds while vulnerabilities linger really hits home. It’s wild how fast AI is reshaping every layer of tech, and audio is no exception. I’ve been experimenting with sound scene creation lately, and tools like Seed Audio 1.0 can spin up entire scenes—dialogue, ambience, effects—from a single prompt. Curious how security concerns might apply to AI-generated media too. sound scene creation
you gotta try Drake burning bridges ai video at https://burningbridgesmv.org/. Thats really interesting
Finding a spot that blends fun with reliability is never easy but this place nails it every single time. I played for a few hours straight and never once dealt with a glitch or a long wait. The staff is warm and helpful whenever I had a quick question. Truly a gem for casual and serious players alike. Discover it today bdtbatbd
The payout speed here is actually impressive. I didn’t expect such a quick turnaround. Really happy with the service at phwinph555
The mobile version runs like butter and I love how quick the cashout options are. It feels like having a personal gaming assistant right in my pocket. Reliable speeds and clear game rules make my playtime stress free.
Elisabetta Franchi en Cannes 2026 suena a elegancia italiana bien entendida, con esa mezcla de sofisticación y carácter que define la Costa Azul. Si te gustan los retos diarios mientras lees sobre moda, dlenow reúne puzzles de palabras, geografía y cine con reglas y consejos útiles.
The fan page explains how to play, controls, and browser requirements. 2f46dc34.
Players can press Esc to leave the game and return to the site. 509c99a5.
The pixel-art style gives the Pokemon world a retro feel. 5268cd7f.
It is satisfying to find a rhythm that brings the sounds together. b27c589f.
Wide-angle mobile lenses exaggerate forward-projecting features like the nose tip while compressing temple width. Running test headshots through looksmaxscale.com/attractiveness-test shows how stepping back to standard portrait distances normalizes facial proportions for analysis.
The point about ‘Excessive Agency’ really resonates — granting AI agents too much autonomy without a human-in-the-loop seems like the risk teams most often overlook. Curious how the community plans to approach testing the ‘Black Box’ nature of LLM outputs in future sessions.
The discussion around vulnerability assessments in AI-driven workflows hits close to home. Teams are adopting internal tools faster than ever, and mapping out the actual surface area and access levels during security reviews has become much more complicated over the past year.
From my end building front-end prototypes, that usually means keeping visual assets and wireframes strictly sandboxed. When I needed a quick sample dashboard for our security audit deck, I used GPT Image 2.5 to generate the interface cards; it took two or three tries to get the spacing right, but the status labels on the panels rendered legibly enough to use without redrawing them in Figma.
This place reminds me of those weekend gatherings with good friends where laughter and luck mix perfectly. Every update brings something fresh yet keeps that warm familiar touch I cherish. Reliable and always genuine. Find it at npstakes
The discussion regarding software vulnerability assessment highlights the critical need for robust security frameworks as generative AI tools accelerate the development process.
The discussion on software vulnerability assessments during the AI era highlights the critical need for robust security frameworks. Balancing the speed of automated code generation with long-term safety protocols is a significant challenge for modern engineering teams.
Focusing on The Session Agenda: Career Resilience: Anupama’s 30-year journey from Enterprise Architect clarifies the trade-off better than a vague summary. Separately, if you want a short break, krillion.me is a free browser word game with no download.
The point about “excessive agency” really hit home—giving AI agents too much autonomy without human verification is a disaster waiting to happen. I’ve been experimenting with an ai flyer maker lately, and even that makes me double-check outputs before publishing. Garuda sounds promising for startups priced out of enterprise tools.
Focusing on The Session Agenda: Career Resilience: Anupama’s 30-year journey from Enterprise Architect clarifies the trade-off better than a vague summary. Separately, if you want a short break, noillirk.app is a daily word-guessing game with no download.
The discussion on balancing the speed of AI-generated code with the long-term security implications highlights a critical challenge for modern software development. I work on CloneCut, an AI video tool.